


Current FCSS_EFW_AD-7.6 Exam Dumps [2026] Complete Fortinet Exam Smoothly
FCSS_EFW_AD-7.6 Premium PDF & Test Engine Files with 92 Questions & Answers
Fortinet FCSS_EFW_AD-7.6 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
NEW QUESTION # 13
Refer to the exhibit, which shows an ADVPN network.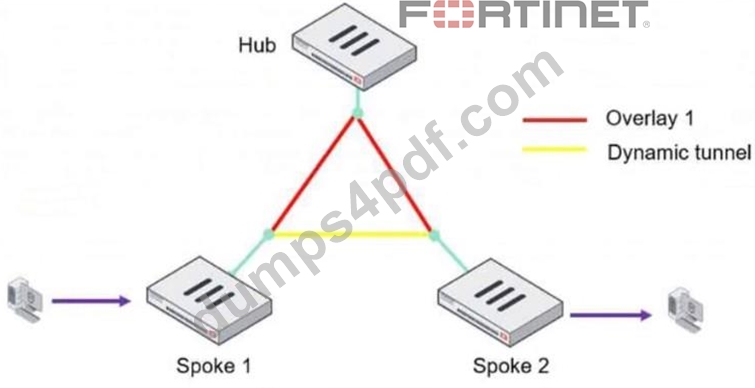
The client behind Spoke-1 generates traffic to the device located behind Spoke-2.
What is the first message that the hub sends to Spoke-1 to bring up the dynamic tunnel?
- A. Shortcut reply
- B. Shortcut query
- C. Shortcut forward
- D. Shortcut offer
Answer: D
Explanation:
In an ADVPN (Auto-Discovery VPN) network, a dynamic VPN tunnel is established on-demand between spokes to optimize traffic flow and reduce latency.
Process:
1. Traffic Initiation:
A client behind Spoke-1 sends traffic to a device behind Spoke-2.
The traffic initially flows through the hub, following the pre-established overlay tunnel.
2. Hub Detection:
The hub detects that Spoke-1 is communicating with Spoke-2 and determines that a direct shortcut tunnel between the spokes can optimize the connection.
3. Shortcut Offer:
The hub sends a "Shortcut Offer" message to Spoke-1, informing it that a direct dynamic tunnel to Spoke-
2 is possible.
4. Tunnel Establishment:
Spoke-1 and Spoke-2 then negotiate and establish a direct IPsec tunnel for communication.
NEW QUESTION # 14
Refer to the exhibit, which shows a partial enterprise network.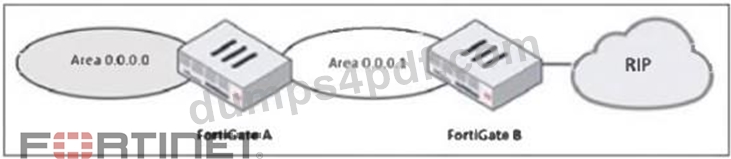
An administrator would like the area 0.0.0.0 to detect the external network.
What must the administrator configure?
- A. Set the area 0.0.0.l type to stub on FortiGate A and B.
- B. Enable RIP redistribution on FortiGate B.
- C. Configure a virtual link between FortiGate A and B.
- D. Configure a distribute-route-map-in on FortiGate B.
Answer: B
Explanation:
The diagram shows a multi-area OSPF network where:
# FortiGate A is in OSPF Area 0 (Backbone area).
# FortiGate B is in OSPF Area 0.0.0.1 and is connected to an RIP network.
To ensure that OSPF Area 0 (0.0.0.0) learns routes from the external RIP network, FortiGate B must redistribute RIP routes into OSPF.
Steps to achieve this:
1. Enable route redistribution on FortiGate B to inject RIP-learned routes into OSPF.
2. This allows OSPF Area 0.0.0.1 to forward RIP routes to OSPF Area 0 (0.0.0.0), making the external network visible.
NEW QUESTION # 15
An administrator is setting up an ADVPN configuration and wants to ensure that peer IDs are not exposed during VPN establishment.
Which protocol can the administrator use to enhance security?
- A. Opt for SSL VPN web mode because it does not use peer IDs at all.
- B. Choose IKEv1 aggressive mode because it simplifies peer identification.
- C. Stick with IKEv1 main mode because it offers better performance.
- D. Use IKEv2, which encrypts peer IDs and prevents exposure.
Answer: D
Explanation:
In ADVPN (Auto-Discovery VPN) configurations, security concerns include protecting peer IDs during VPN establishment. Peer IDs are exchanged in the IKE (Internet Key Exchange) negotiation phase, and their exposure could lead to privacy risks or targeted attacks. IKEv2 encrypts peer IDs, making it more secure compared to IKEv1, where peer IDs can be exposed in plaintext in aggressive mode.
IKEv2 also provides better performance and flexibility while supporting dynamic tunnel establishment in ADVPN.
NEW QUESTION # 16
An administrator is designing an ADVPN network for a large enterprise with spokes that have varying numbers of internet links. They want to avoid a high number of routes and peer connections at the hub.
Which method should be used to simplify routing and peer management?
- A. Establish a traditional hub-and-spoke VPN topology with policy routes.
- B. Implement static routing over IPsec interfaces for each spoke.
- C. Use a dynamic routing protocol using loopback interfaces to streamline peers and routes.
- D. Deploy a full-mesh VPN topology to eliminate hub dependency.
Answer: C
Explanation:
When designing an ADVPN (Auto-Discovery VPN) network for a large enterprise with spokes that have varying numbers of internet links, the main challenge is to minimize the number of peer connections and routes at the hub while maintaining scalability and efficiency.
Using a dynamic routing protocol (such as BGP or OSPF) with loopback interfaces helps in several ways:
# Reduces the number of peer connections at the hub by using a single loopback address per spoke instead of individual physical interfaces.
# Enables simplified route advertisement by dynamically learning and propagating routes instead of manually configuring static routes.
# Supports multiple internet links per spoke efficiently, as dynamic routing can automatically adjust to the best available path.
# Allows seamless failover if a spoke's internet link fails, ensuring continuous connectivity.
NEW QUESTION # 17
An administrator configured the FortiGate devices in an enterprise network to join the Fortinet Security Fabric. The administrator has a list of IP addresses that must be blocked by the data center firewall. This list is updated daily.
How can the administrator automate a firewall policy with the daily updated list?
- A. With FortiAnalyzer
- B. With an external connector from Threat Feeds
- C. With FortiNAC
- D. With a Security Fabric automation
Answer: B
Explanation:
The best way to automate a firewall policy using a daily updated list of IP addresses is by using an external connector from Threat Feeds. This allows FortiGate to dynamically retrieve real-time threat intelligence from external sources and apply it directly to security policies.
By configuring Threat Feeds, the administrator can:
# Automatically update firewall policies with the latest malicious IPs daily.
# Block traffic from those IPs in real-time without manual intervention.
# Integrate with FortiGuard, third-party threat intelligence sources, or custom feeds (CSV, STIX
/TAXII, etc.).
NEW QUESTION # 18
An administrator must enable direct communication between multiple spokes in a company's network. Each spoke has more than one internet connection.
The requirement is for the spokes to connect directly without passing through the hub, and for the links to automatically switch to the best available connection.
How can this automatic detection and optimal link utilization between spokes be achieved?
- A. Implement SD-WAN policies at the hub to manage spoke link quality.
- B. Establish static VPN tunnels between spokes with predefined backup routes.
- C. Set up OSPF routing over static VPN tunnels between spokes.
- D. Utilize ADVPN 2.0 to facilitate dynamic direct tunnels and automatic link optimization.
Answer: D
Explanation:
ADVPN (Auto-Discovery VPN) 2.0 is the optimal solution for enabling direct spoke-to-spoke communication without passing through the hub, while also allowing automatic link selection based on quality metrics.
# Dynamic Direct Tunnels:
# ADVPN 2.0 allows spokes to establish direct IPsec tunnels dynamically based on traffic patterns, reducing latency and improving performance.
# Unlike static VPNs, spokes do not need to pre-configure tunnels for each other.
# Automatic Link Optimization:
# ADVPN 2.0 monitors the quality of multiple internet connections on each spoke.
# It automatically switches to the best available connection when the primary link degrades or fails.
# This is achieved by dynamically adjusting BGP-based routing or leveraging SD-WAN integration.
NEW QUESTION # 19
An administrator must minimize CPU and RAM use on a FortiGate firewall while also enabling essential security features, such as web filtering and application control for HTTPS traffic.
Which SSL inspection setting helps reduce system load while also enabling security features, such as web filtering and application control for encrypted HTTPS traffic?
- A. Configure SSL inspection to handle HTTPS traffic efficiently.
- B. Use full SSL inspection to thoroughly inspect encrypted payloads.
- C. Enable SSL certificate inspection mode to perform basic checks without decrypting traffic.
- D. Disable SSL inspection entirely to conserve resources.
Answer: C
Explanation:
To minimize CPU and RAM usage while still enforcing security features like web filtering and application control, SSL certificate inspection mode is the best choice.
# SSL certificate inspection allows FortiGate to inspect only the SSL/TLS handshake, including the Server Name Indication (SNI) and certificate details, without decrypting the full encrypted payload.
# This enables features like web filtering and application control because FortiGate can determine the destination website or application based on SNI and certificate information.
# It significantly reduces system load compared to full SSL inspection, which requires full decryption and re-encryption of traffic.
NEW QUESTION # 20
Refer to the exhibit.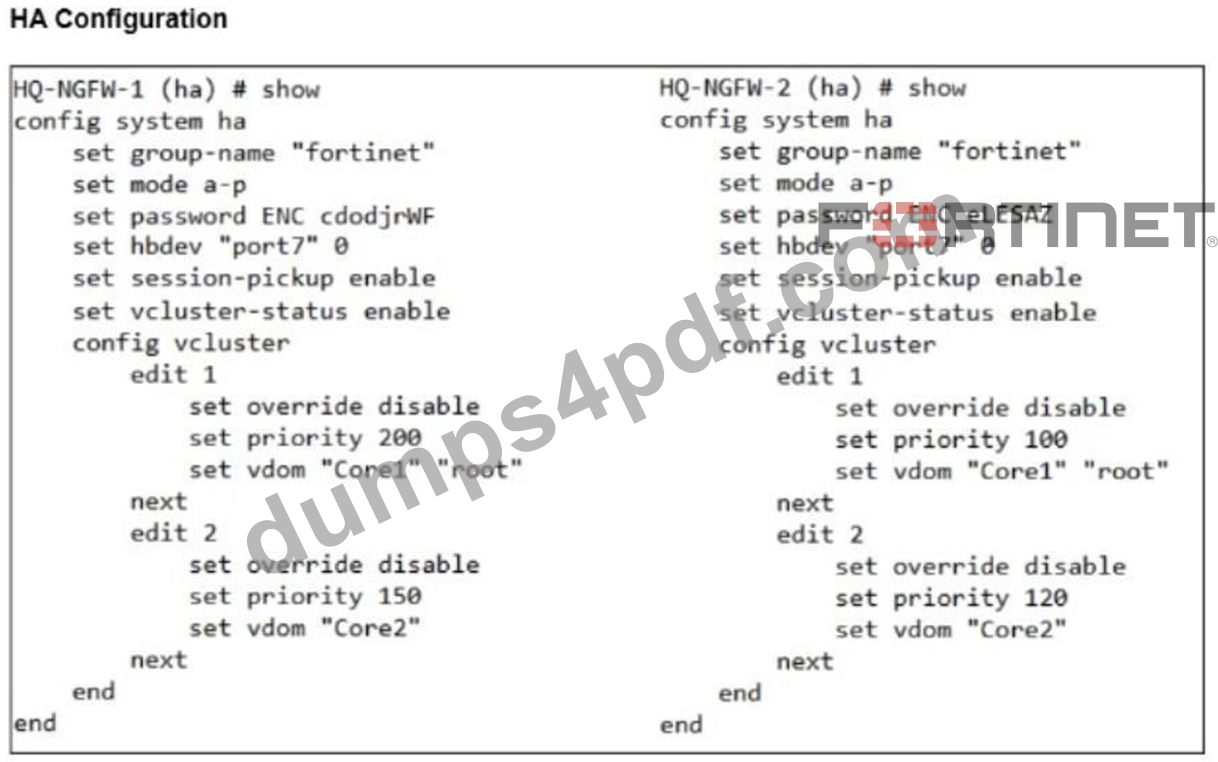
An HA configuration of an active-active (A-A) cluster with the same HA uptime shown.
You want HQ-NGFW-2 to handle the Core2 VDOM traffic.
Which modification must you make to achieve this outcome?
- A. Enable override in virtual duster 2 for HQ-NGFW-2.
- B. Change the priority from 100 to 160 for HQ-NGFW-2.
- C. Change the priority from 120 to 200 for HQ-NGFW-2.
- D. Reboot HQ-NGFW-2.
Answer: C
Explanation:
In an A-A setup using virtual clusters, each VDOM belongs to a vcluster and the device with the higher priority becomes the primary for that vcluster. For Core2, HQ-NGFW-1 currently has priority 150 and HQ-NGFW-2 has 120. To make HQ-NGFW-2 the primary for Core2, its vcluster-2 priority must be raised above 150, and increasing it to 200 achieves that.
NEW QUESTION # 21
An administrator is checking an enterprise network and sees a suspicious packet with the MAC address e0:23:
ff:fc:00:86.
What two conclusions can the administrator draw? (Choose two.)
- A. The suspicious packet is related to a cluster with a group-id value lower than 255.
- B. The network includes FortiGate devices configured with the FGSP protocol.
- C. The suspicious packet is related to a cluster that has VDOMs enabled.
- D. The suspicious packet corresponds to port 7 on a FortiGate device.
Answer: C,D
Explanation:
According to the FortiOS 7.6 Infrastructure study guide and High Availability (HA) documentation, FortiGate units in an HA cluster use a virtual MAC address to ensure seamless failover. The structure of this virtual MAC address is strictly defined by the Fortinet HA protocol.
For a standard HA cluster, the virtual MAC address format is 00:09:0f:09:<group-id_hex>:
<vcluster_port_hex>. However, when VDOMs are enabled, the virtual MAC address prefix changes to e0:
23:ff to accommodate the additional complexity of multiple virtual domains. Therefore, the prefix e0:23:ff in the suspicious MAC address e0:23:ff:fc:00:86 confirms that the packet originated from a cluster with VDOMs enabled (Option A).
Regarding the interface identification, the last byte (86) is calculated as follows:
* The 0x80 bit indicates virtual-cluster 2 (vcluster 2). Since $0x86 = 0x80 + 0x06$, we know the packet is from vcluster 2.
* The remaining value 0x06 represents the interface index. In FortiOS, the index starts at 0 (port1 = 0, port2 = 1, port3 = 2, port4 = 3, port5 = 4, port6 = 5, port7 = 6). Therefore, the index 6 corresponds exactly to port 7 (Option D).
The fourth byte (fc) represents the HA Group ID (252 in decimal). While this is indeed lower than 255, the specific logic of the virtual MAC composition in a VDOM-enabled environment points specifically to the port identification and vcluster status as the primary diagnostic conclusions.
NEW QUESTION # 22
Which statement about meta fields is true?
- A. Meta fields must be set to required.
- B. Meta fields are useful for creating multiple objects with the same logical name but different values.
- C. Meta fields can be used as variables in scripts or provisioning templates.
- D. Meta field changes are applied only at the ADOM level.
Answer: B
Explanation:
Meta fields are useful when an enterprise has global offices or branches and the FortiManager administrator must creation multiple objects with the same logical name, but different values.
NEW QUESTION # 23
Refer to the exhibit, which shows a command output.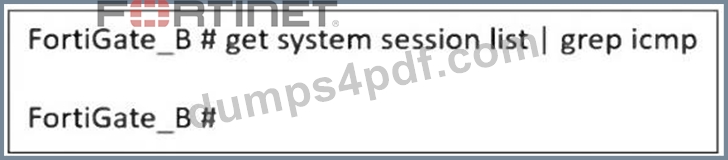
FortiGate_A and FortiGate_B are members of an FGSP cluster in an enterprise network.
While testing the cluster using the ping command, the administrator monitors packet loss and found that the session output on FortiGate_B is as shown in the exhibit.
What could be the cause of this output on FortiGate_B?
- A. FortiGate_B is configured in passive mode.
- B. FortiGate_A and FortiGate_B have the same standalone-group-id value.
- C. session-pickup-connectionless is set to disable on FortiGate_B.
- D. The session synchronization is encrypted.
Answer: C
Explanation:
The Fortinet FGSP (FortiGate Session Life Support Protocol) cluster allows session synchronization between two FortiGate devices to provide seamless failover. However, ICMP (ping) is a connectionless protocol, and by default, FortiGate does not synchronize connectionless sessions unless explicitly enabled.
In the exhibit:
# The command get system session list | grep icmp on FortiGate_B returns no output, meaning that ICMP sessions are not being synchronized from FortiGate_A.
# If session-pickup-connectionless is disabled, FortiGate_B will not receive ICMP sessions, causing packet loss during failover.
NEW QUESTION # 24
A vulnerability scan report has revealed that a user has generated traffic to the website example.com (10.10.10.10) using a weak SSL/TLS version supported by the HTTPS web server.
What can the firewall administrator do to block all outdated SSL/TLS versions on any HTTPS web server to prevent possible attacks on user traffic?
- A. Install the required certificate in the client's browser or use Active Directory policies to block specific websites as defined in the SSL/SSH inspection profile.
- B. Enable auto-detection of outdated SSL/TLS versions in the SSL/SSH inspection profile to block vulnerable websites.
- C. Use the latest certificate, Fortinet_SSL_ECDSA256, and replace the CA certificate in the SSL/SSH inspection profile.
- D. Configure the unsupported SSL version and set the minimum allowed SSL version in the HTTPS settings of the SSL/SSH inspection profile.
Answer: D
Explanation:
The best way to block outdated SSL/TLS versions is to configure the SSL/SSH inspection profile to enforce a minimum SSL/TLS version and disable weak SSL versions.
By setting the minimum allowed SSL version in the HTTPS settings of the SSL/SSH inspection profile, FortiGate will:
# Block any connection using outdated SSL/TLS versions (such as SSLv3, TLS 1.0, or TLS 1.1).
# Enforce secure communication using only strong SSL/TLS versions (such as TLS 1.2 or TLS 1.3).
# Protect users from man-in-the-middle (MITM) and downgrade attacks that exploit weak encryption.
NEW QUESTION # 25
Refer to the exhibits.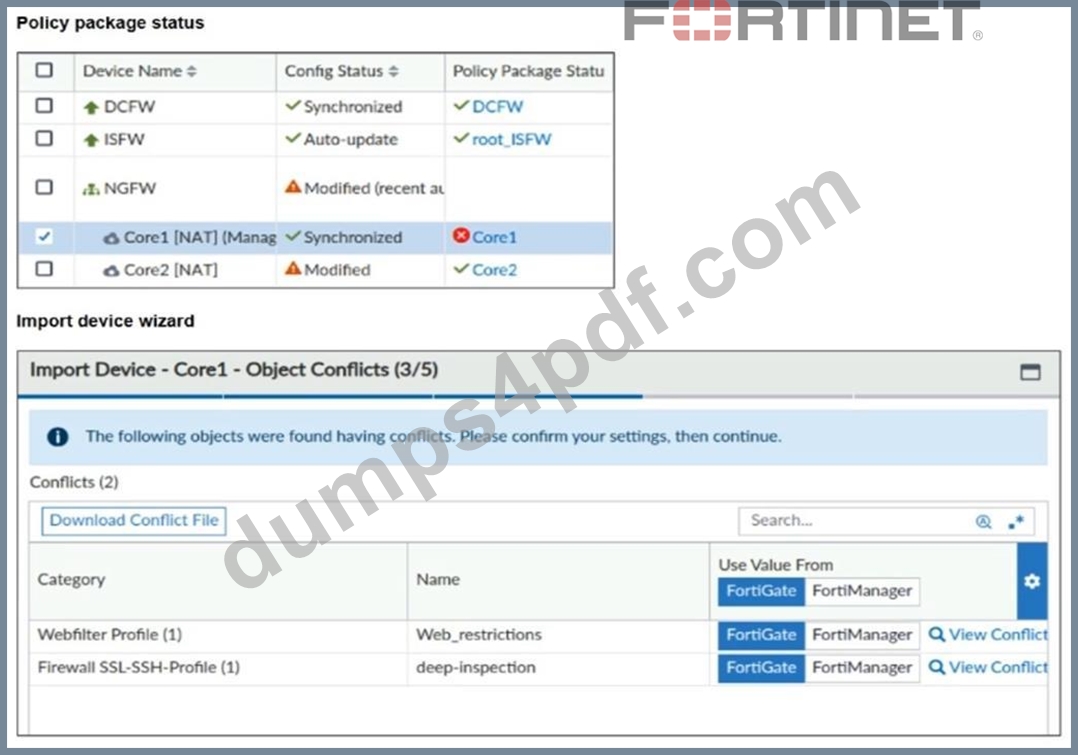
A policy package conflict status and information from the import device wizard in the Core1 VDOM are shown.
When you import a policy package, the following message appears for the Web_restrictions web filter profile and the deep-inspection SSL-SSH profile:
The following objects were found having conflicts. Please confirm your
settings, then continue.
The Web_restrictions and deep-inspection profiles are used by other FortiGate devices within FortiManager.
Which step must you take to resolve the issue?
- A. Create uniquely named objects on FortiGate and reimport them into the policy package.
- B. Use non-default object values because FortiManager is unable to alter default values.
- C. Select the FortiManager configuration that accepts changes on FortiManager and preserves existing configurations on FortiGate devices.
- D. Retrieve the FortiGate configuration to automatically export correct objects and policies.
Answer: C
Explanation:
Since the conflicting objects already exist on FortiManager and are shared by multiple devices, the correct approach is to keep the FortiManager version of those objects. Selecting the FortiManager configuration resolves the conflict and preserves centralized object consistency without overwriting shared objects with device-specific versions.
NEW QUESTION # 26
An administrator must enable direct communication between multiple spokes in a company's network. Each spoke has more than one internet connection. The requirement is for the spokes to connect directly without passing through the hub, and for the links to automatically switch to the best available connection. How can this automatic detection and optimal link utilization between spokes be achieved?
- A. Implement SD-WAN policies at the hub to manage spoke link quality.
- B. Establish static VPN tunnels between spokes with predefined backup routes.
- C. Set up OSPF routing over static VPN tunnels between spokes.
- D. Utilize ADVPN 2.0 to facilitate dynamic direct tunnels and automatic link optimization.
Answer: D
Explanation:
ADVPN (Auto-Discovery VPN) 2.0 is the optimal solution for enabling direct spoke-to-spoke communication without passing through the hub, while also allowing automatic link selection based on quality metrics.
Dynamic Direct Tunnels:
ADVPN 2.0 allows spokes to establish direct IPsec tunnels dynamically based on traffic patterns, reducing latency and improving performance.
Unlike static VPNs, spokes do not need to pre-configure tunnels for each other.
Automatic Link Optimization:
ADVPN 2.0 monitors the quality of multiple internet connections on each spoke. It automatically switches to the best available connection when the primary link degrades or fails.
This is achieved by dynamically adjusting BGP-based routing or leveraging SD-WAN integration.
NEW QUESTION # 27
Refer to the exhibits.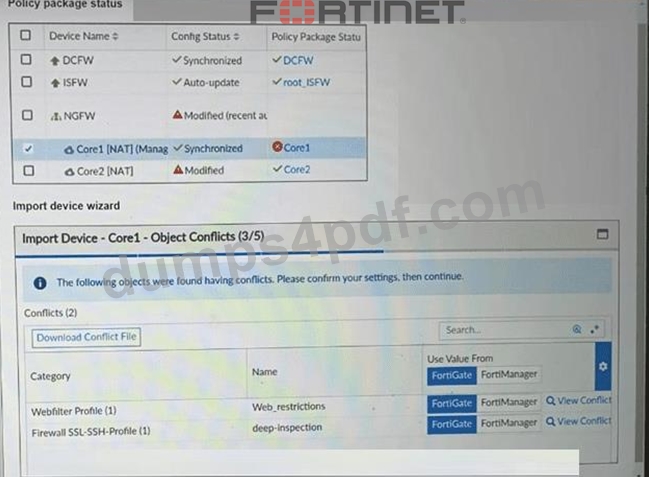
A policy package conflict status and information from the import device wizard in the Core1 VDOM are shown. When you import a policy package, the following message appears for the Web_restrictions web filter profile and the deep-inspection SSL-SSH profile: "The following objects were found having conflicts.
Please confirm your settings, then continue." The Web_restrictions and deep-inspection profiles are used by other FortiGate devices within FortiManager. Which step must you take to resolve the issue? (Choose one answer)
- A. Create uniquely named objects on FortiGate and reimport them into the policy package.
- B. Use non-default object values because FortiManager is unable to alter default values.
- C. Select the FortiManager configuration that accepts changes on FortiManager and preserves existing configurations on FortiGate devices.
- D. Retrieve the FortiGate configuration to automatically export correct objects and policies.
Answer: A
Explanation:
Comprehensive and Detailed 150 to 200 words of Explanation From Exact Extract of Enterprise Firewall 7.6 Administrator documents:
According to the FortiManager 7.6 Study Guide regarding Object Management and the Import Device Wizard, FortiManager uses a centralized database where objects are shared across an ADOM. When importing a configuration from a FortiGate, the wizard compares local objects with those already existing in the FortiManager ADOM database.
As shown in the exhibit, conflicts exist for the Web_restrictions and deep-inspection profiles. Since these profiles are shared with other FortiGate devices, a decision must be made:
* Selecting "FortiManager": The local FortiGate settings will be overwritten by the FortiManager's database version upon the next installation, potentially losing site-specific configurations.
* Selecting "FortiGate": The FortiManager ADOM database is updated with the new values. This causes all other FortiGate devices using these shared objects to move into a "Modified" status, as their local configurations no longer match the updated central database.
To resolve this conflict properly when different devices require different settings for the same profile type, the best practice is to create uniquely named objects (Option B) on the FortiGate before re-importing. This ensures that the specific requirements for the Core1 VDOM are met without affecting the global objects used by the rest of the enterprise network.
NEW QUESTION # 28
An administrator is checking an enterprise network and sees a suspicious packet with the MAC address e0:23:ff:fc:00:86.
What two conclusions can the administrator draw? (Choose two.)
- A. The suspicious packet corresponds to port 7 on a FortiGate device.
- B. The suspicious packet is related to a cluster with a group-id value lower than 255.
- C. The network includes FortiGate devices configured with the FGSP protocol.
- D. The suspicious packet is related to a cluster that has VDOMs enabled.
Answer: B,D
Explanation:
The MAC address e0:23:ff:fc:00:86 follows the format used in FortiGate High Availability (HA) clusters. When FortiGate devices are in an HA configuration, they use virtual MAC addresses for failover and redundancy purposes.
The suspicious packet is related to a cluster that has VDOMs enabled:
FortiGate devices with Virtual Domains (VDOMs) enabled use specific MAC address ranges to differentiate HA-related traffic. This MAC address is likely part of that mechanism.
The suspicious packet is related to a cluster with a group-id value lower than 255:
FortiGate HA clusters assign virtual MAC addresses based on the group ID. The last octet (00:86) corresponds to a group ID that is below 255, confirming this option.
NEW QUESTION # 29
Refer to the exhibit, which shows the packet capture output of a three-way handshake between FortiGate and FortiManager Cloud.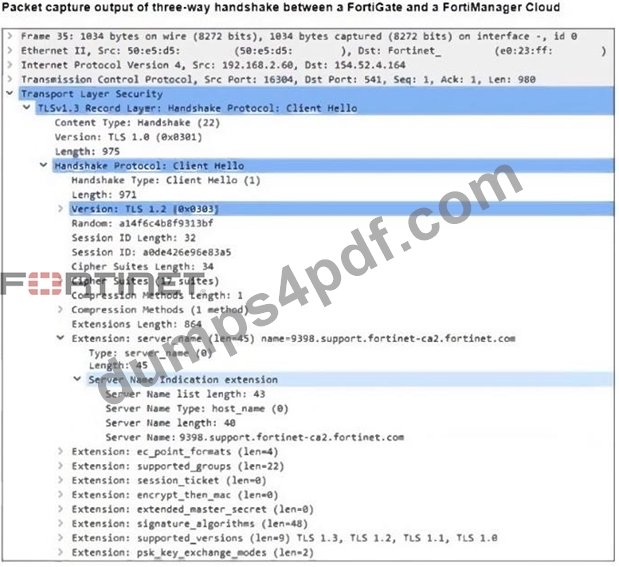
What two conclusions can you draw from the exhibit? (Choose two.)
- A. FortiGate is connecting to the same IP server and will receive an independent certificate for its connection between FortiGate and FortiManager Cloud.
- B. The wildcard for the domain *.fortinet-ca2.support.fortinet.com must be supported by FortiManager Cloud.
- C. If the TLS handshake contains 17 cipher suites it means the TLS version must be 1.0 on this three-way handshake.
- D. FortiGate will receive a certificate that supports multiple domains because FortiManager operates in a cloud computing environment.
Answer: B,D
NEW QUESTION # 30
Refer to the exhibit, which contains a partial VPN configuration.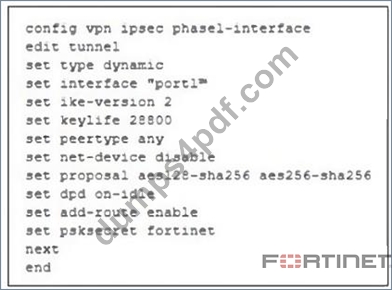
What can you conclude from this VPN IPsec phase 1 configuration?
- A. Peer IDs are unencrypted and exposed, creating a security risk.
- B. A separate interface is created for each dial-up tunnel, which can be slower and more resource intensive, especially in large networks.
- C. FortiGate will not add a route to its routing or forwarding information base when the dynamic tunnel is negotiated.
- D. This configuration is the best for networks with regular traffic intervals, providing a balance between connectivity assurance and resource utilization.
Answer: D
Explanation:
This IPsec Phase 1 configuration defines a dynamic VPN tunnel that can accept connections from multiple peers. The settings chosen here suggest a configuration optimized for networks with intermittent traffic patterns while ensuring resources are used efficiently.
Key configurations and their impact:
# set type dynamic # This allows multiple peers to establish connections dynamically without needing predefined IP addresses.
# set ike-version 2 # Uses IKEv2, which is more efficient and supports features like EAP authentication and reduced rekeying overhead.
# set dpd on-idle # Dead Peer Detection (DPD) is triggered only when the tunnel is idle, reducing unnecessary keep-alive packets and improving resource utilization.
# set add-route enable # FortiGate automatically adds the route to the routing table when the tunnel is established, ensuring connectivity when needed.
# set proposal aes128-sha256 aes256-sha256 # Uses strong encryption and hashing algorithms, ensuring a secure connection.
# set keylife 28800 # Sets a longer key lifetime (8 hours), reducing the frequency of rekeying, which is beneficial for stable connections.
Because DPD is set to on-idle, the tunnel will not constantly send keep-alive messages but will still ensure connectivity when traffic is detected. This makes the configuration ideal for networks with regular but non- continuous traffic, balancing security and resource efficiency.
NEW QUESTION # 31
An administrator wants to scale the IBGP sessions and optimize the routing table in an IBGP network.
Which parameter should the administrator configure?
- A. network-import-check
- B. ibgp-enforce-multihop
- C. route-reflector-client
- D. neighbor-group
Answer: C
Explanation:
In an IBGP (Internal BGP) network, all routers must be fully meshed, meaning every router must establish a BGP session with every other router in the same autonomous system (AS). This does not scale well in large networks due to the exponential increase in BGP sessions.
To optimize and scale IBGP, Route Reflectors (RRs) are used. A Route Reflector (RR) reduces the number of IBGP peer connections by allowing a centralized router (RR) to redistribute IBGP routes to other IBGP peers (called clients). This eliminates the need for a full mesh, significantly reducing BGP session overhead.
By configuring the route-reflector-client setting on IBGP peers, an administrator can:
Scale IBGP sessions by reducing the number of direct BGP peer connections. Optimize the routing table by ensuring routes are efficiently propagated within the IBGP network. Eliminate the need for full mesh topology, making IBGP more manageable.
NEW QUESTION # 32
An administrator configured the following command on FortiGate.
config router ospf
set restart-mode graceful-restart
Which two statements correctly describe the result of the above command? (Choose two.)
- A. FortiGate is configured with graceful restart, and will exit graceful mode, if the network topology changes.
- B. The OSPF neighbor that receives the grace link-state advertisement (LSA) will enter into helper mode.
- C. After the default 40 seconds wait time, the OSPF neighbors will resume communication with the restarting router.
- D. In an HA cluster, FortiGate devices will keep the OSPF routes in their routing table to avoid traffic interruption during an HA failover.
Answer: B,D
NEW QUESTION # 33
Refer to the exhibit, which shows a partial troubleshooting command output.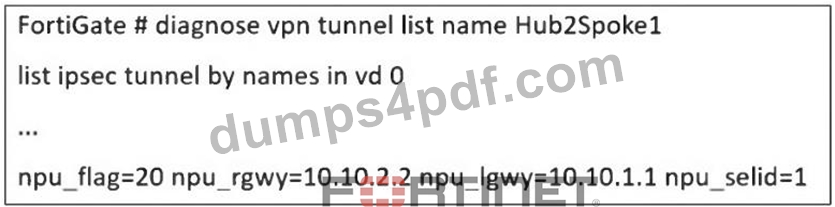
An administrator is extensively using IPsec on FortiGate. Many tunnels show information similar to the output shown in the exhibit.
What can the administrator conclude?
- A. The two IPsec SAs, inbound and outbound, are copied to the NPU.
- B. IPsec SAs cannot be offloaded.
- C. Only the outbound IPsec SA is copied to the NPU.
- D. Only the inbound IPsec SA is copied to the NPU.
Answer: A
Explanation:
The diagnose vpn tunnel list name Hub2Spoke1 command output provides key information about the offloading status of an IPsec VPN tunnel to the Network Processing Unit (NPU).
# npu_flag=20:
# This flag indicates that both inbound and outbound IPsec Security Associations (SAs) have been offloaded to the NPU, meaning the VPN traffic is processed in hardware instead of the CPU.
# npu_rgwy=10.10.2.2 and npu_lgwy=10.10.1.1:
# These IPs represent the remote gateway (rgwy) and local gateway (lgwy), confirming that the tunnel is successfully offloaded.
# npu_selid=1:
# This value means the session selector for the NPU offloaded SA is active.
Since both inbound and outbound SAs are offloaded, the administrator can conclude that the FortiGate NPU is handling IPsec encryption and decryption efficiently, reducing CPU load and improving VPN performance.
NEW QUESTION # 34
Refer to the exhibit, which shows a hub and spokes deployment.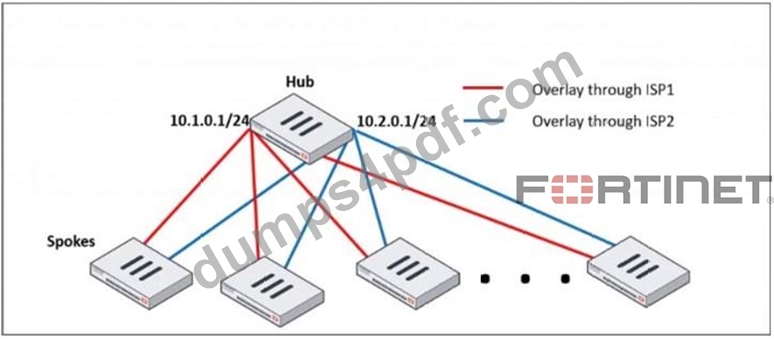
An administrator is deploying several spokes, including the BGP configuration for the spokes to connect to the hub.
Which two commands allow the administrator to minimize the configuration? (Choose two.)
- A. ibgp-enforce-multihop
- B. route-reflector-client
- C. neighbor-range
- D. neighbor-group
Answer: C,D
Explanation:
neighbor-group:
# This command is used to group multiple BGP neighbors with the same configuration, reducing redundant configuration.
# Instead of defining individual BGP settings for each spoke, the administrator can create a neighbor-group and apply the same policies, reducing manual work.
neighbor-range:
# This command allows the configuration of a range of neighbor IPs dynamically, reducing the need to manually define each spoke neighbor.
# It automatically adds BGP neighbors that match a given prefix, simplifying deployment.
NEW QUESTION # 35
An administrator received a FortiAnalyzer alert that a 1 ## disk filled up in a day. Upon investigation, they found thousands of unusual DNS log requests, such as JHCMQK.website.com, with no answers. They later discovered that DNS exfiltration was occurring through both UDP and TLS.
How can the administrator prevent this data theft technique?
- A. Use an IPS profile and DNS exfiltration-related signatures.
- B. Configure a File Filter profile to prevent DNS exfiltration.
- C. Enable DNS Filter to protect against DNS exfiltration.
- D. Create an inline-CASB to protect against DNS exfiltration.
Answer: A
Explanation:
The excessive DNS log requests with random subdomains suggest a DNS exfiltration attack, where attackers encode and transmit data via DNS queries. Since this technique can use both UDP and TLS (DoH - DNS over HTTPS), a comprehensive security approach is needed.
Using an IPS profile with DNS exfiltration-specific signatures allows FortiGate to:
# Detect and block abnormal DNS query patterns often used in exfiltration.
# Inspect encrypted DNS (DoH, DoT) traffic if SSL inspection is enabled.
# Identify known exfiltration domains and techniques based on FortiGuard threat intelligence.
NEW QUESTION # 36
Refer to the exhibit, which shows a command output.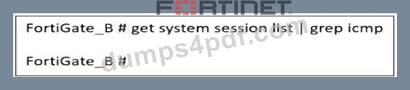
FortiGate_A and FortiGate_B are members of an FGSP cluster in an enterprise network.
While testing the cluster using the ping command, the administrator monitors packet loss and found that the session output on FortiGate_B is as shown in the exhibit.
What could be the cause of this output on FortiGate_B?
- A. FortiGate_B is configured in passive mode.
- B. FortiGate_A and FortiGate_B have the same standalone-group-id value.
- C. session-pickup-connectionless is set to disable on FortiGate_B.
- D. The session synchronization is encrypted.
Answer: C
Explanation:
The Fortinet FGSP (FortiGate Session Life Support Protocol) cluster allows session synchronization between two FortiGate devices to provide seamless failover. However, ICMP (ping) is a connectionless protocol, and by default, FortiGate does not synchronize connectionless sessions unless explicitly enabled.
In the exhibit:
The command get system session list | grep icmp on FortiGate_B returns no output, meaning that ICMP sessions are not being synchronized from FortiGate_A. If session-pickup-connectionless is disabled, FortiGate_B will not receive ICMP sessions, causing packet loss during failover.
NEW QUESTION # 37
......
FCSS_EFW_AD-7.6 Premium Files Practice Valid Exam Dumps Question: https://pass4sure.dumps4pdf.com/FCSS_EFW_AD-7.6-valid-braindumps.html